Documented information
Policies, procedures and records with coding, revisions and a multi-level approval workflow. Each document can be linked to the clauses of the standard.
ISO 27001
An information security management system lives on approved policies, audits, corrective actions and tracked training. SGQM manages this part, with automatic deadlines and reminders.
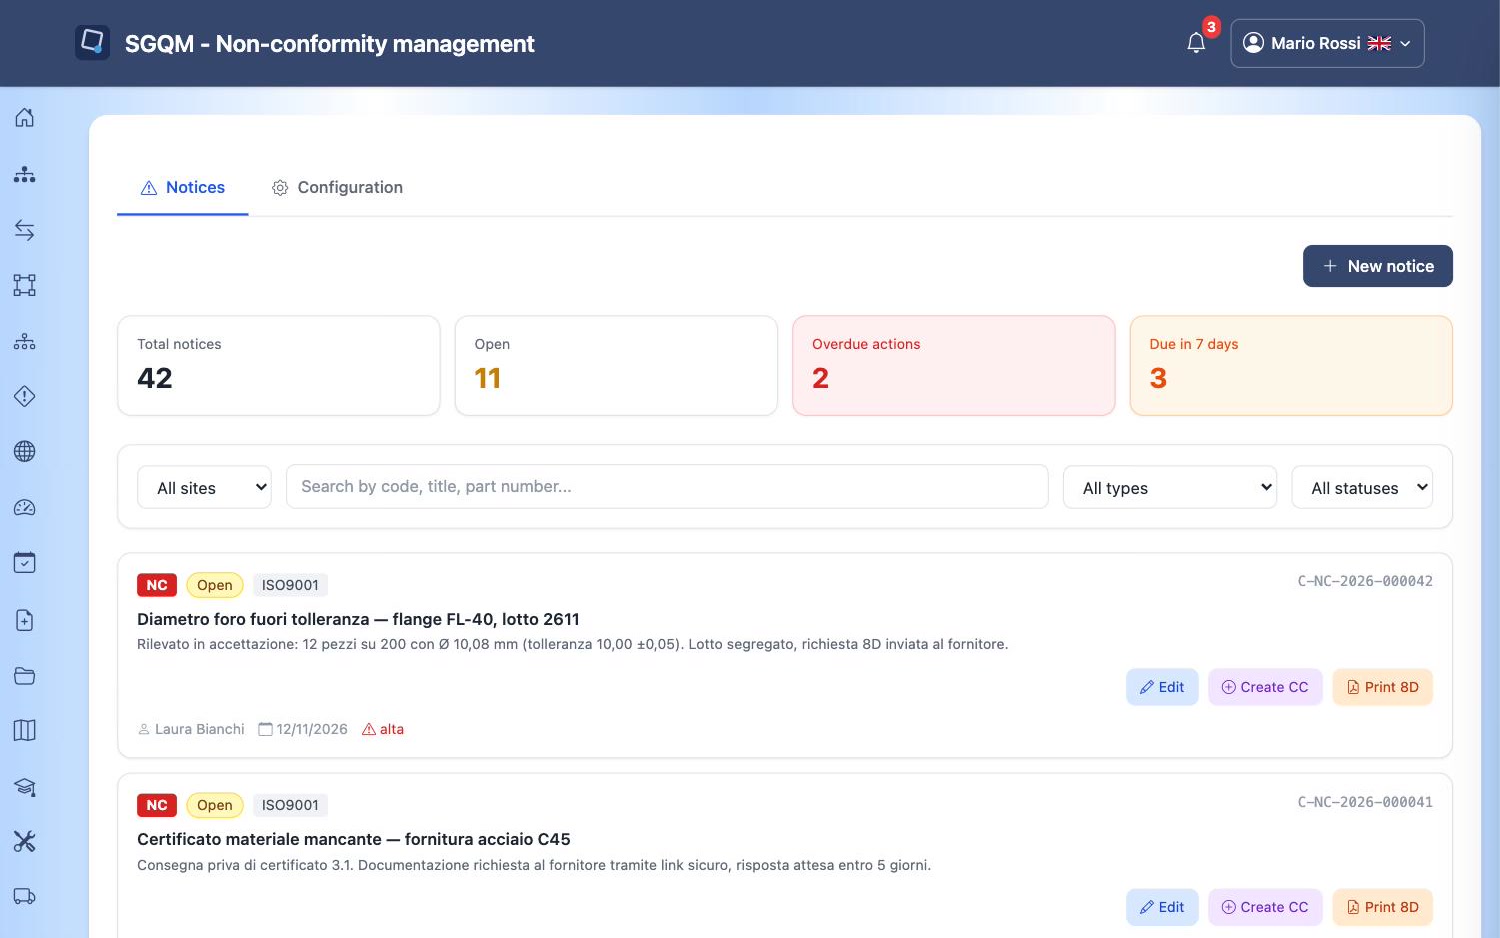
Beyond technical controls, ISO 27001 asks you to show that the system is governed: up-to-date documents, trained people, audits carried out, nonconformities closed. This is the work SGQM makes orderly and verifiable.
Policies, procedures and records with coding, revisions and a multi-level approval workflow. Each document can be linked to the clauses of the standard.
Training plan and course records on information security, with monitored deadlines.
Planning, evidence and findings of audits, linked to corrective actions.
Report, root cause analysis, actions and closure check in the same record, with owners and due dates.
Supplier register and evaluation. For reports that concern them, they reply through a protected, expiring link, without accessing your system.
Document reviews and recurring activities go into the deadline tracker and are chased automatically.
No. SGQM does not replace technical tools such as antivirus, SIEM or vulnerability management. It manages the organisational side of the system: documents, audits, actions, training and deadlines.
SGQM is a cloud web service. For details on hosting and security measures, ask in your demo request and we will go through them together.
Yes. Several standards live in the same integrated system, sharing documents, audits and actions.
Contact
Fill in the form and we'll get back to you within 24 hours to arrange a personalised demo.